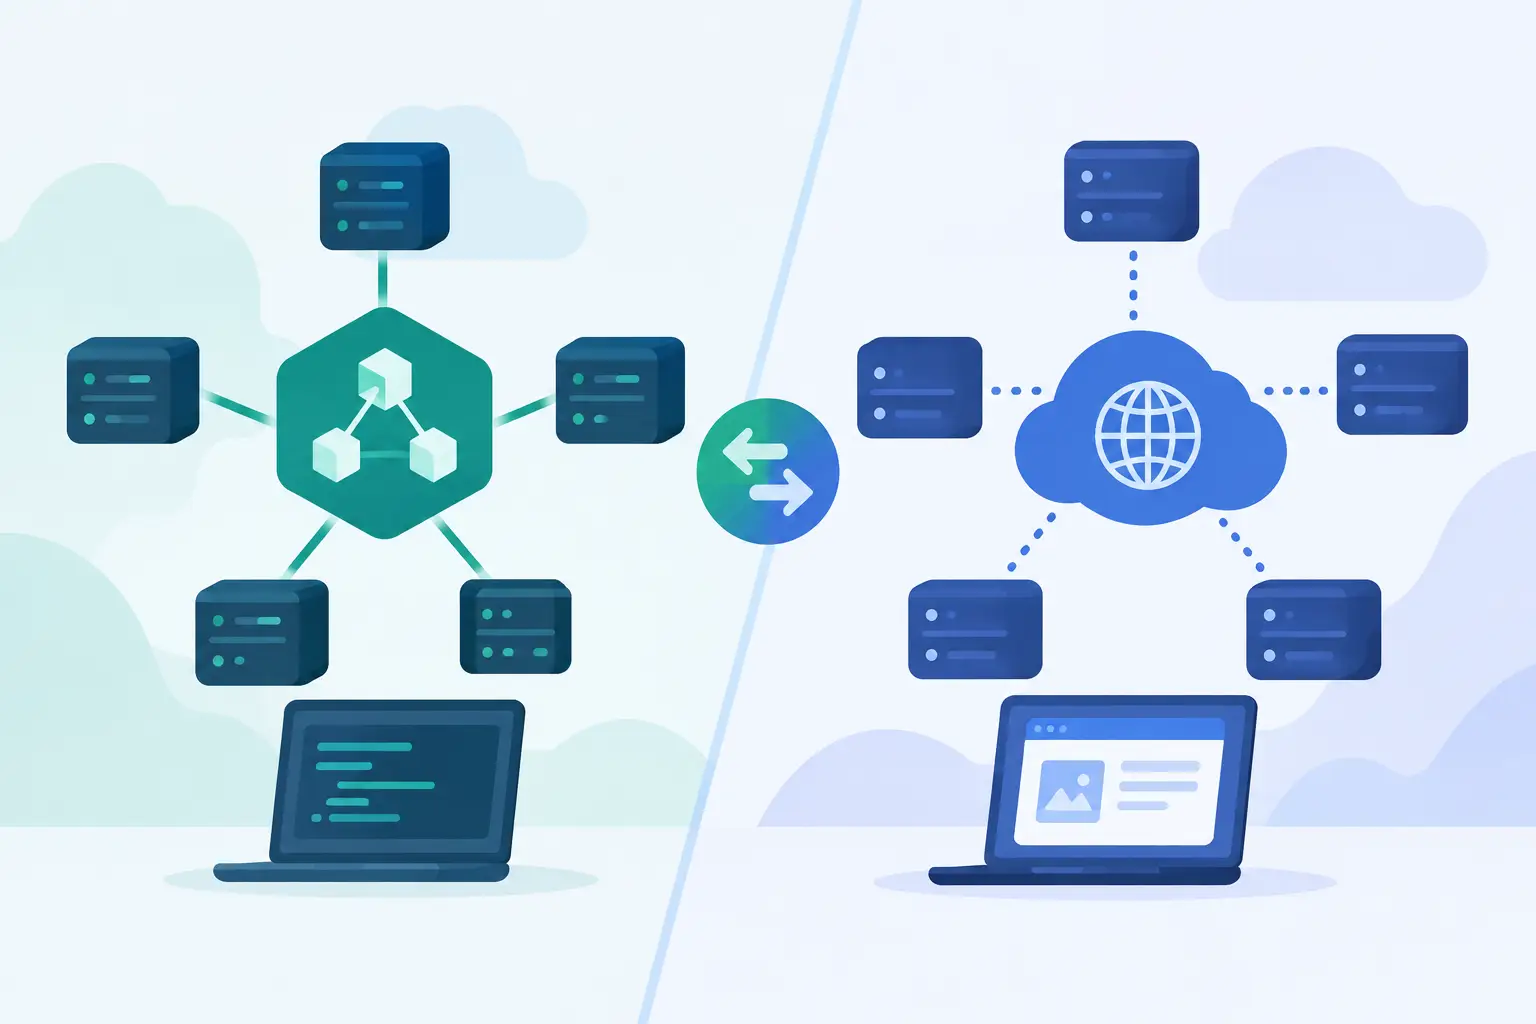
A mobile app needs a fast, predictable backend call. A public developer platform needs an API that anyone can test with a browser and curl. Those are different jobs, which is why the gRPC versus REST decision should start with the consumers and operating environment, not a benchmark chart.
REST remains the default language of web APIs for good reasons: it is familiar, visible, broadly compatible, and easy to inspect. gRPC brings a different set of strengths: strongly typed contracts, generated clients, efficient binary messages, and first-class streaming. Neither is automatically the modern answer. The better choice is the one that reduces friction for the systems and people that must use it.
gRPC versus REST at a Glance
REST is an architectural style built around resources and standard HTTP semantics. A typical REST API exposes URLs such as `/orders/123`, uses methods such as GET, POST, PATCH, and DELETE, and commonly sends JSON. JSON is a convention rather than a requirement, but it is the format most teams expect.
gRPC is a remote procedure call framework. Teams define services and messages in Protocol Buffers, then generate client and server code from that contract. Instead of requesting a resource URL, a client calls a method such as `GetOrder` or `CreateOrder`. gRPC typically uses HTTP/2 and Protocol Buffers, a compact binary serialization format.
The distinction is more than syntax. REST tends to optimize for broad interoperability and resource-oriented public interfaces. gRPC tends to optimize for controlled service-to-service communication, where both sides can adopt shared tooling and a formal contract.
Performance Is More Than Payload Size
gRPC often uses less bandwidth than JSON-based REST because Protocol Buffers encode data in binary form. Generated serializers can also reduce CPU work compared with parsing large JSON documents. HTTP/2 supports multiplexed streams over one connection, which can help services that make many concurrent calls.
Those gains are real, but they are not a universal reason to replace REST. For an API that spends most of its time waiting on a database, a third-party service, or a cold serverless function, serialization may be a small part of the total latency. Compression can narrow payload differences as well. A well-designed REST endpoint that returns only needed fields may outperform a poorly designed gRPC service that triggers expensive downstream work.
Streaming is where gRPC can create a clearer advantage. It supports server streaming, client streaming, and bidirectional streaming as part of its programming model. That is useful for live telemetry, collaborative systems, event ingestion, device communication, and long-running AI or data-processing workflows. REST can support streaming through techniques such as server-sent events or chunked responses, but gRPC makes the interaction part of the service contract.
Contracts and Developer Experience
Protocol Buffers give gRPC one of its biggest practical benefits: a schema is central to the workflow. A `.proto` definition specifies message fields, service methods, and data types. From there, teams can generate clients for languages such as Go, Java, C#, Python, TypeScript, and more. This reduces hand-written request models and catches many integration mismatches before runtime.
That contract-driven approach is valuable in large microservice estates. When dozens of services are maintained by separate teams, generated clients can make API consumption more consistent and make changes easier to review. Field numbers in Protocol Buffers also support deliberate evolution. Teams can add optional fields without breaking older consumers, provided they do not reuse retired field numbers or casually change a field’s meaning.
REST can be contract-first too. OpenAPI specifications, JSON Schema, and client generation provide many of the same benefits. The difference is cultural and operational: REST teams are more likely to treat the API description as documentation that follows implementation, while gRPC workflows naturally place the schema at the center. Either model works when the contract is versioned, tested in CI, and treated as a compatibility commitment.
Where REST Still Has the Edge
REST is usually the more practical option for public APIs and browser-facing applications. Browsers understand HTTP and JSON natively. Developers can inspect a REST request in standard browser tools, replay it with curl, and experiment with it using common API clients. HTTP caching behavior, status codes, and CDN support are also well understood.
Native browser support is a meaningful boundary for gRPC. Standard browser APIs do not expose all HTTP/2 features that traditional gRPC expects, particularly HTTP/2 trailers. Teams can use gRPC-Web or an alternative protocol layer, but that adds a proxy, compatibility constraints, or extra tooling. If a JavaScript application is the primary consumer, REST is frequently simpler to ship and debug.
REST also maps naturally to platform capabilities such as API gateways, rate limiting, edge caching, and web application firewalls. Those controls are available for gRPC in many cloud and gateway products, but the maturity and day-to-day familiarity of HTTP/JSON tooling still matter. An interface that partners can understand in minutes may be worth more than a smaller payload.
Operational Trade-Offs That Affect the Choice
Observability deserves attention before an API standard is selected. REST traffic is easy to inspect because headers and JSON bodies are readable. gRPC metadata, status codes, and binary payloads require tooling that understands the protocol. Modern tracing platforms support gRPC well, but teams should verify that logs, metrics, traces, load balancers, service meshes, and incident-response tools expose the signals they need.
Error handling differs, too. REST commonly communicates outcomes with HTTP status codes and a JSON error body. gRPC uses a defined status model, with codes such as `NOT_FOUND`, `INVALID_ARGUMENT`, and `UNAVAILABLE`, plus optional details. gRPC’s model can be more consistent inside an organization, but only if teams establish conventions for retries, deadlines, idempotency, and error details.
Security is not inherently better in either approach. Both should use TLS, strong authentication, authorization at the service boundary, input validation, rate limits, and audit trails where needed. With gRPC, pay particular attention to deadlines and message-size limits so a slow or oversized request cannot consume connections indefinitely. With REST, avoid exposing sensitive data through overly broad resource responses, query parameters, or verbose error messages.
Choosing gRPC, REST, or Both
Choose gRPC when low-latency service-to-service communication, generated multi-language clients, strict contracts, or streaming are central requirements. It is especially effective for internal microservices, high-throughput data paths, and systems where teams control both client and server releases.
Choose REST when building public APIs, browser-first products, partner integrations, or interfaces that benefit from human-readable requests and familiar HTTP semantics. It is also the safer default when an organization lacks shared Protocol Buffers tooling or when consumers span unpredictable platforms.
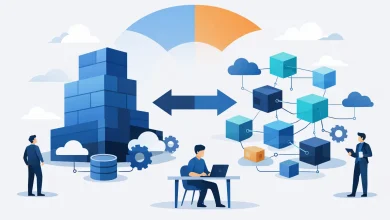
Many mature architectures use both. An external API gateway can expose REST and JSON to web and partner clients, while internal services communicate through gRPC. This is not duplication for its own sake. It separates a stable, accessible edge contract from an efficient internal transport. The key is to avoid creating two independently evolving APIs with inconsistent behavior.
If your team supports both protocols, define ownership carefully. Decide which API is the source of truth, generate or translate where practical, and test that validation rules, authorization, pagination, errors, and versioning behavior remain aligned. HTTP-to-gRPC transcoding can help in some environments, but it does not remove design work. Resource semantics and RPC semantics still need deliberate mapping.
Make the Decision With a Small Pilot
Before standardizing, test a representative workflow rather than a synthetic hello-world endpoint. Include real payload sizes, authentication, service mesh or gateway behavior, retries, tracing, and the slowest downstream dependency. Measure p95 and p99 latency, error rates, developer setup time, and how quickly an engineer can diagnose a failed request.
The winning protocol is the one that makes your system easier to evolve under real constraints. Start with the consumers, make contracts explicit, and select the transport that lets your team deliver reliable changes without turning every integration into a special case.