A leaked API key rarely starts as a dramatic security incident. More often, it begins as a convenience decision: a database password in a local `.env` file, a production token copied into a CI variable, or a shared spreadsheet that outlives the project it was meant to support. The top secrets management tools address that operational gap by giving teams a controlled way to store, deliver, rotate, and audit the credentials that keep software running.
For a DevSecOps team, the right choice is not simply the tool with the longest feature list. It depends on where workloads run, how often credentials change, whether applications need dynamic access, and how much operational ownership the team can realistically take on. A startup operating entirely on one cloud platform has different needs from an enterprise that spans Kubernetes clusters, legacy services, multiple clouds, and regulated environments.
What a Secrets Manager Should Actually Do
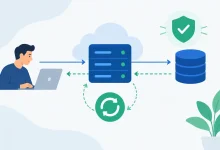
A secrets manager stores sensitive values such as API keys, database credentials, TLS certificates, OAuth client secrets, signing keys, and service-account tokens. Storage is only the baseline. A useful platform also controls who and what can retrieve each secret, records access activity, encrypts data, and supports rotation without forcing engineers to manually edit configuration across every environment.
The distinction between static and dynamic secrets matters. A static secret is created elsewhere and placed in the manager, such as a third-party API token. A dynamic secret is generated when a workload requests access, often with a short expiration time. For example, an application can request a temporary database user valid for one hour rather than receiving a permanent shared database password. Dynamic credentials reduce the blast radius of a leak, but they require deeper integration and more careful application design.
Teams should also separate secrets management from adjacent controls. A password manager helps people safely store and share credentials. A cloud identity platform governs authentication and authorization. A secrets manager is focused on securely delivering machine credentials to applications, pipelines, infrastructure tools, and automation. Some products bridge these categories, but the use case should drive the evaluation.
Top Secrets Management Tools to Consider
HashiCorp Vault
HashiCorp Vault is often the reference point for enterprise-grade secrets management. It supports multiple authentication methods, detailed policies, encryption as a service, transit encryption, and dynamic credentials for systems such as databases and cloud providers. Its flexibility makes it a strong fit for platform teams managing hybrid or multi-cloud environments.
Vault’s main trade-off is operational complexity. Self-hosting requires planning for high availability, storage backends, unsealing, upgrades, monitoring, and disaster recovery. Managed offerings reduce that burden, but teams still need to design policies and authentication flows thoughtfully. Vault is especially compelling when short-lived credentials and centralized policy control are core requirements rather than future aspirations.
AWS Secrets Manager
AWS Secrets Manager is a practical choice for teams whose production workloads already live primarily in AWS. It integrates closely with IAM, AWS Lambda, Amazon RDS, and CloudTrail. Applications running on ECS, EKS, EC2, or Lambda can retrieve secrets using workload identities instead of embedding long-lived cloud access keys.
Its strongest advantage is reduced operational overhead. There is no secrets-management cluster to run, and managed rotation can work well for supported database services. The trade-off is portability. While AWS Secrets Manager can store credentials for external systems, its identity model and deployment experience are most natural inside AWS. Teams with major Azure, Google Cloud, or on-premises footprints may prefer a more neutral control plane.
Azure Key Vault
Azure Key Vault provides secret, key, and certificate management for Microsoft-centric environments. It works closely with Microsoft Entra ID, Azure Managed Identities, Azure Kubernetes Service, and Azure DevOps. That integration allows services to authenticate without application teams carrying cloud credentials in configuration.
Key Vault is particularly effective when an organization already standardizes on Azure identity and resource governance. Its role-based access controls and audit integration help security teams apply familiar Azure policies to sensitive configuration. As with other cloud-native options, the practical question is whether Azure is the primary runtime environment. If it is, Key Vault keeps the architecture straightforward; if it is only one part of a broad estate, cross-cloud access patterns deserve early testing.
Google Cloud Secret Manager
Google Cloud Secret Manager is designed for applications running in Google Cloud, with granular IAM permissions, versioned secrets, audit logs, and integrations across GKE, Cloud Run, and other managed services. Versioning is useful when rolling out a new credential gradually or recovering quickly after a failed rotation.
For GCP-focused teams, the service offers a clear and low-maintenance path. Workload Identity can remove the need to distribute service-account keys to Kubernetes workloads, which is a major security improvement. The limitation is familiar: it is optimized for Google Cloud’s identity and operational model, not for organizations looking for a single independent layer across every environment.
Doppler
Doppler focuses on developer experience and environment configuration. It gives teams a central way to organize secrets by project and environment, synchronize them to supported cloud platforms, and make local development less dependent on manually maintained `.env` files. For teams that want developers to adopt better habits without creating a heavy platform project, that usability can be valuable.
Doppler is strongest for managing application configuration consistently across development, staging, and production. It may be less suitable than Vault for advanced dynamic-secret workflows or complex enterprise authorization models. Still, its emphasis on easy adoption makes it a credible option for product teams that need control quickly and cannot dedicate engineers to operating a specialized security service.
1Password Secrets Automation
1Password Secrets Automation extends a familiar credential-management model into service accounts, command-line workflows, and automated secret injection. It can be especially useful when the same organization needs a safer way for employees and software delivery systems to handle credentials without maintaining separate tools for every audience.
This approach can reduce the temptation to move secrets through chat, tickets, or unmanaged documents. It is a good fit for developer teams that already use 1Password and want a practical route to CI/CD and infrastructure automation. For highly regulated workloads requiring complex dynamic database credentials or large-scale policy engines, a dedicated platform such as Vault or CyberArk Conjur may offer more specialized controls.
Infisical and CyberArk Conjur
Infisical is an option for teams that want an open-source-friendly developer secrets platform with self-hosting possibilities. Its appeal is a modern workflow for application configuration, environment separation, and team collaboration. It can be a sensible fit for organizations that value deployment control but want a gentler learning curve than a fully customized Vault implementation.
CyberArk Conjur is built for enterprise and machine-identity use cases, particularly where privileged access management, compliance requirements, and containerized workloads intersect. It is worth evaluating when security governance is a primary buying driver and the organization already has a broader CyberArk footprint. The trade-off is that its enterprise focus can introduce more planning and administration than smaller engineering teams need.
How to Choose Among Secrets Management Tools
Start with identity, not storage. Ask how an application proves its identity before it receives a secret. Kubernetes service accounts, cloud workload identities, OpenID Connect tokens from CI systems, and machine certificates are generally safer than distributing static bootstrap credentials. If a tool requires another permanent secret just to retrieve the first secret, the design deserves scrutiny.
Next, map the delivery paths. A secret might be needed by a local developer, a GitHub Actions job, Terraform, a Kubernetes pod, a serverless function, and a legacy virtual machine. A platform that looks excellent for one path can create friction in another. Test the actual retrieval flow before committing, including failure behavior when a secret is unavailable or rotated.
Rotation is another dividing line. If credentials rarely change, secure storage and access auditing may be sufficient at first. If database accounts, cloud tokens, or certificates need frequent rotation, prioritize native lifecycle automation and application support for credential refresh. Rotating a password is not useful if every service must be restarted manually and half the fleet continues using a cached value.
Finally, measure administrative cost honestly. A self-hosted platform can provide control, but it also becomes a security-critical service that needs patching, backups, alerts, access reviews, and recovery exercises. A managed cloud service can reduce that work, though it may deepen provider dependence. Neither choice is universally better.
Implementation Practices That Prevent Common Failures
Adopting a tool is not the same as improving secrets hygiene. Begin by inventorying where secrets exist now: source repositories, CI variables, shared drives, deployment scripts, local environment files, and vendor dashboards. Rotate exposed values as they are discovered rather than merely moving them into a new system.
Use least-privilege policies at the workload level. A billing service should not retrieve payment-provider credentials for every other application, and a staging deployment should never have a path to production secrets. Environment separation, narrowly scoped service identities, and readable policy naming make reviews easier later.
Avoid exposing secrets through logs, error reports, process listings, or generated build artifacts. Secret scanning in repositories and CI pipelines is still necessary because accidental disclosure can happen before a secrets manager enters the picture. Audit logs should answer who or what accessed a value, from where, and under which identity.
The most effective secrets strategy is the one engineers can use correctly under delivery pressure. Select a tool that fits your infrastructure, make secure access the easiest path, and treat every credential rotation as a chance to remove one more permanent trust relationship from your software.